

Simulated attacks to find and fix vulnerabilities.


Managed Cyber Security Services
Your security operations, run for you, 24/7.
Technetics Cyber Security provides managed cyber security services for Melbourne and Australian businesses that need round-the-clock protection without building an internal security team. We monitor your systems 24/7, investigate threats, coordinate response and report on what matters.


What are managed cyber security services?
Security alerts need someone to investigate them. Vulnerabilities need an owner. When something suspicious happens at 2am, your team needs a plan. That is what our managed service delivers.
Managed cyber security services are ongoing services where a specialist provider monitors your systems, investigates threats and maintains your security controls on your behalf. The provider is called a managed security service provider, or MSSP.
Two parts sit at the core:
- Security operations centre (SOC): the analysts and processes that monitor, investigate and respond to threats.
- Security information and event management (SIEM): the platform that collects logs from your systems and flags suspicious activity.
The outcome is clear coverage, fast action and someone accountable for security every hour of the day. Your business still owns its risk decisions and takes part in agreed response and remediation work.


At a glance
24/7 monitoring through our managed SOC and SIEM
Alert triage within 2 minutes, with critical threats escalated within 15 minutes
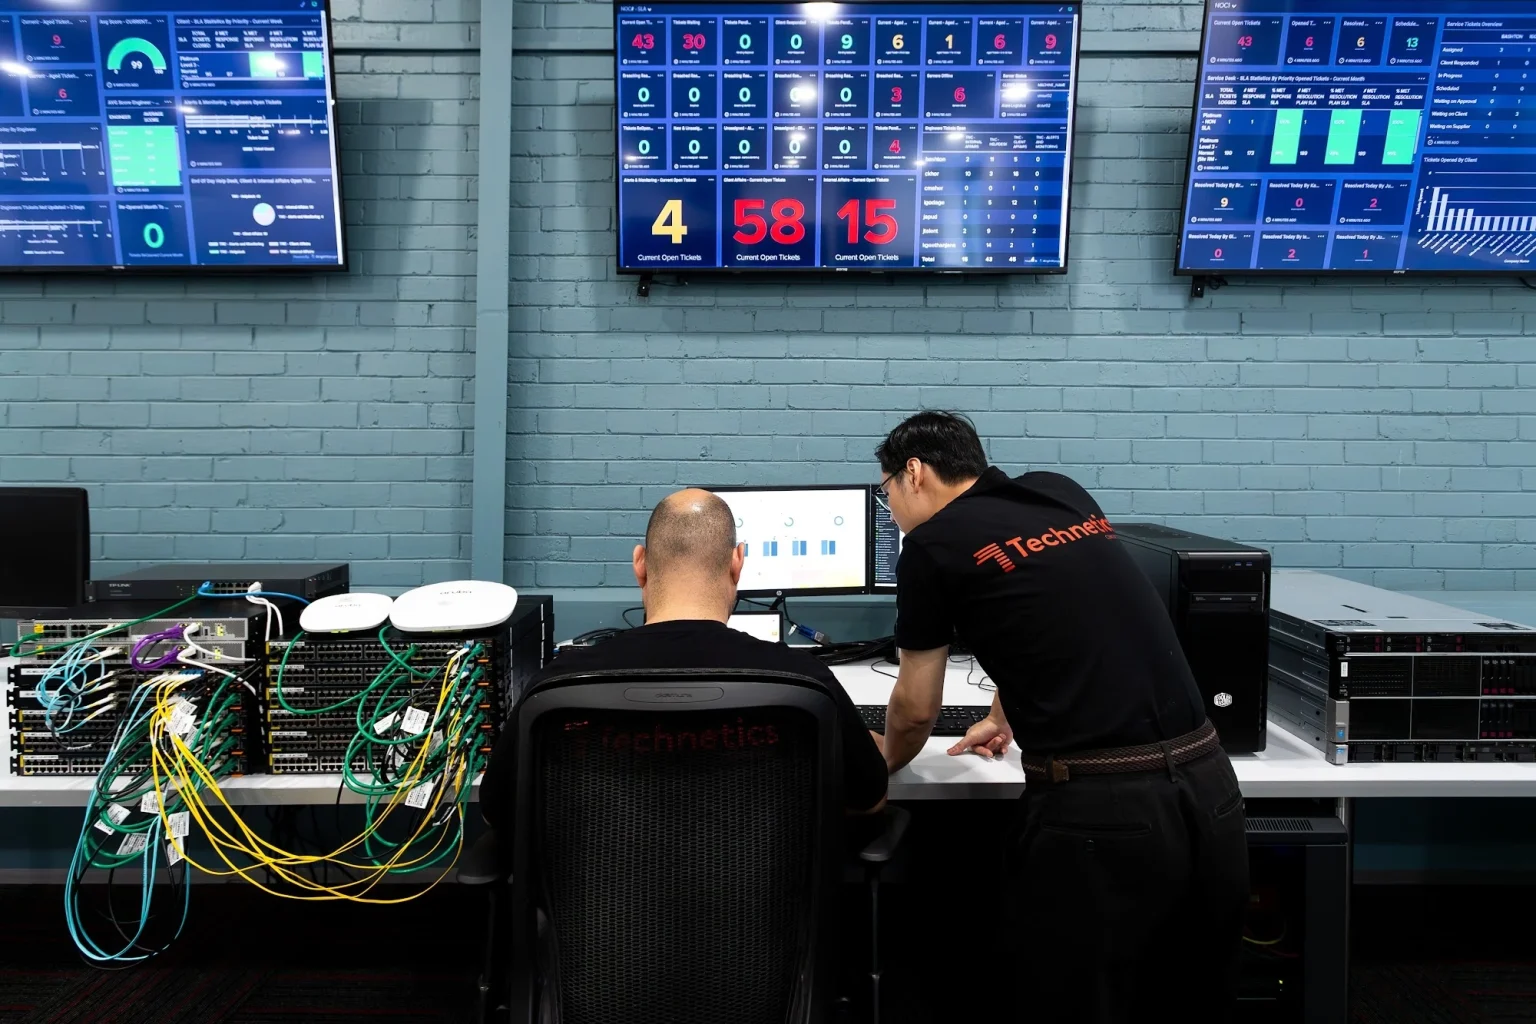
Australian-based team in South Melbourne
Monthly reporting your leadership team can act on
Works with your existing IT provider and security tools
Put clear ownership behind your security tools
You may already have endpoint protection, cloud security tools and an IT provider. The questions remain: who reviews the alerts, who follows up findings and who acts when a threat is confirmed?
Our managed cyber security service answers all three. We agree the systems in scope, what we monitor and how escalation works, so security information turns into action.
Our managed SOC and SIEM service provides 24/7 monitoring and threat investigation. Protection, remediation and advisory work can be added to match your requirements.
Signs you need managed security
- Your tools generate more alerts than your team can investigate.
- Security responsibilities are split across several providers and nobody owns the gaps.
- Nobody watches your systems after hours or on weekends.
- A customer review or insurance renewal exposed missing evidence.
- Your business added users, remote access or cloud services faster than security kept up.
- A recent incident showed your escalation process does not work.
Managed security gives these activities consistent attention. Your IT team gets specialist backup. Leadership gets visibility of open actions. Staff get clear instructions for reporting suspicious activity.
What our managed cyber security service covers
We build the service around your environment, existing tools and priorities. Final inclusions, coverage and response times are set out in your service agreement.
24/7 monitoring
Monitoring of agreed security data sources through our managed SOC and SIEM
Managed detection and response (MDR)
Investigation, threat validation, escalation and agreed containment actions
Endpoint security
Management of protections across covered laptops, desktops and servers
Vulnerability and patch management
Finding exposures, prioritising updates and coordinating or delivering fixes
Email and identity security
Monitoring account protections, suspicious sign-ins and email security controls
Cloud security
Monitoring and configuration review for Microsoft 365, Azure and other in-scope cloud services
Reporting and improvement
Monthly reporting on incidents, findings, open actions and recommended changes
Backup management, restore testing, staff training and Essential 8 assessments can be added. Setting these boundaries upfront makes it easy to compare proposals on the work that will actually be delivered.
How we respond to a threat
Collect
We connect agreed data sources such as endpoints, servers, network devices and cloud platforms to our SIEM. We confirm what is covered and flag any gaps that limit detection.
Investigate
Our analysts review each alert in context and separate real threats from normal activity. Confirmed threats are ranked by severity and business impact.
Escalate and contain
Your response plan sets out who we contact and which actions we are authorised to take. That can include isolating a device, disabling a compromised account or coordinating containment with your IT team.
Review and improve
Every incident improves future protection. Reporting highlights recurring issues, unresolved weaknesses and changes to detection rules, so each month your environment is harder to attack.
Client result
Airmet Scientific supplies scientific monitoring equipment and works with customers in defence and other sensitive industries. Its communications and shared documents require strong security, making cyber security expertise a key reason they chose Technetics. That support became tangible one Friday evening when a suspicious login attempt triggered an account lock and a direct call from Technetics. Despite it being after hours, the team investigated, called back about 10 minutes later, and restored access. Operations Director Gavin Slee described how the prompt response kept work moving, demonstrating responsive security support that helps maintain business continuity beyond normal office hours.
“Obviously, cyber security has become a much bigger piece of the puzzle. I know with Technetics, one of the reasons we went there was because of that strength.”
Simon Meers, Director, Airmet Scientific
Client Success Stories
Technetics have been our trusted IT partner for over 13 years, growing alongside our business and helping us work smarter every step of the way. Their proactive approach, technical expertise, and reliability have delivered real improvements to our efficiency and bottom line. They’re not just a provider — they’re an essential part of our success.
Andrew Dunne
Director, Advertising Associates

Since Technetics took over the management of our technology and cyber security, there hasn’t been a single incident! Having worked with other firms in the past, I can confidently say they are top tier when it comes to service and partnership.
Kim Dema
CFO, Harris Capital


After suffering a cyber attack that held our data ransom, we turned to Technetics for help. Their solution completely transformed our IT setup — from messy and unreliable to streamlined, secure, and efficient. We now operate without downtime, and with total peace of mind. Zoran and his team truly feel like partners in our business growth.
Adam Fletcher
CEO, CR Labs


Oliver Hume
3 years ago
Fantastic experience with the team at Technetics, they really took the effort to understand our requirements and provided quality solutions for our business. Highly recommended!

Ani D
3 years ago
This is great company to work with. Great communication, reliable, good response times and patient. The team are willing to learning the organisations needs and give the most current and fitting advice in all things I.T related. John, Ruby, Mario and Justin, I have really appreciated working with you and the rest of the Technetics staff since I started at the BUV.
Keep up the good work.

Michelle Keating
4 years ago
Secure site, and knowledgeable service.

Minh Si
4 years ago
Great service, have been dealing with Technetics for past year and will always go back
Works alongside your existing IT team
Internal IT teams already manage users, systems, projects and support tickets. Managed security adds specialist capability and a clear process for handling security findings.
We agree responsibilities before the service starts. In one setup, your IT provider deploys patches and restores systems while Technetics monitors, investigates and advises. In another, we take on more of the operational work.
Ownership matters most for privileged access, urgent updates and after-hours decisions. Your team will know who approves a disruptive action and how to reach the right people.
Managed cyber security for your industry
The threats are much the same across sectors. What changes is who asks for evidence, what data you hold and how much security help you have in-house.
Defence supply chain
Defence primes and government customers increasingly ask suppliers to show how they protect sensitive information, often against the Essential Eight or the Defence Industry Security Program (DISP). We monitor your environment, track remediation and keep the evidence a security review asks for. Airmet Scientific, which supplies customers in defence, chose Technetics partly for its cyber security strength.
Professional services
Law firms, accounting practices and financial advisers hold confidential client records and often move money on clients’ behalf, which makes them a prime target for business email compromise and invoice fraud. We watch for suspicious sign-ins and email activity, contain compromised accounts under your agreed response plan, and report in the form insurers and clients ask for.
Not-for-profits
Not-for-profits hold donor, member and client data, often with a small IT budget, shared devices, and staff and volunteers working remotely. A managed service gives you specialist monitoring and response without hiring a security team, for a predictable monthly fee, with reporting your board can follow.
Managed security provider or internal security team?
For most small and medium-sized businesses, a managed provider delivers 24/7 coverage at a fraction of the cost of an internal team. Larger organisations often use both, with the managed service covering after-hours monitoring and specialist investigation.
| Consideration | Building internally | Using a managed provider |
|---|---|---|
| People | Recruit, train and retain scarce security staff | Access a full team of analysts from day one |
| Coverage | 24/7 cover needs at least five full-time staff on a roster | 24/7 monitoring and escalation included |
| Technology | Buy, integrate and maintain SIEM and security tools | SIEM platform included, existing tools integrated |
| Response | Build and practise your own procedures | Tested response procedures, agreed with your team |
| Cost | Salaries, licences, training and overheads | Predictable monthly fee plus any agreed project work |
Reporting your leadership team can use
Leadership needs to know which risks need attention and whether agreed actions are being completed. Our monthly reports cover:
Significant security events and how they were handled
Open investigations and their status
Unresolved vulnerabilities and who owns them
Actions needed from your team
Any gaps in visibility or coverage
We link findings to decisions. Repeated alerts on one account may trigger an access review. Recurring patch failures may reveal a device management problem. We agree reporting frequency and audience during onboarding.
Support for your Essential 8 program
Managed security keeps your Essential 8 controls working day to day: reviewing access, catching missed updates and tracking remediation.
An Essential 8 assessment does a different job. It evaluates your implementation against a maturity target. Monitoring alone does not establish a maturity level. If compliance is driving your enquiry, we can scope both the assessment and the ongoing work. See our Essential 8 compliance services.
How much do managed cyber security services cost?
Managed cyber security with Technetics starts from $59 per user per month + GST. Pricing depends on the number of users and devices, systems in scope, coverage hours and how much operational work we take on. Cloud environments, log volumes and integration needs also affect cost.
Across the Australian market, managed security is priced per user, per device or as a fixed monthly fee. When comparing quotes, separate the recurring fee from onboarding, licensing and project work, and ask:
- What happens during a serious incident, and is it included?
- Which remediation tasks are included?
- Is extra investigation or recovery work charged separately?
We scope the service around your environment before quoting, including the tools you already own.
Getting started
Onboarding typically takes 1 to 2 weeks.
Bring your existing IT provider into the discussion if they will share delivery responsibilities.
Discovery call
We learn about your business, current security and why you are looking at managed services.
Scope and quote
We define the systems, services and responsibilities to include. An assessment can help where priorities are unclear.
Onboarding
We set up access, integrations, contacts and your response plan.
Go live
Monitoring and reporting are tested, then the ongoing service begins.
Give your security operations a clear owner
Tell us what you have in place, where your team needs support and what you need a security partner to take on. We will design a managed cyber security service that fits your environment, with clear responsibilities and a quote you can compare.
Get a Managed Security Quote Call 1300 130 730
Managed cyber security questions answered
What is the difference between an MSP and an MSSP?
An MSP (managed service provider) runs general IT: helpdesk, devices, networks and software. An MSSP (managed security service provider) specialises in security: monitoring, threat investigation and managing security controls. Some providers offer both. Compare the actual scope and response arrangements, not the label.
Do you provide 24/7 monitoring?
Yes. Technetics provides 24/7 managed SOC and SIEM monitoring. Your agreement lists the covered systems, monitoring arrangements and escalation process. Round-the-clock monitoring does not automatically mean every IT task or recovery activity is included after hours. Those responsibilities are defined during scoping.
What is managed detection and response (MDR)?
MDR combines threat detection with investigation and hands-on response, such as isolating an infected device. When comparing MDR services, check which systems are covered, who investigates, what containment the provider is authorised to perform and how escalation works.
Can we keep our existing security software?
Usually, yes. We assess your current tools during onboarding for compatibility, configuration and visibility. If we recommend a change, we explain the gap it fixes and any licensing or migration cost.
Does managed security include patching?
It can. Some services find missing updates and coordinate fixes with your IT provider. Others include deploying patches on agreed systems. Your agreement sets out who deploys urgent fixes, who tests changes and who follows up failures, so no vulnerability sits unresolved between providers.
Can managed security guarantee we will not be breached?
No provider can guarantee that. Managed security improves visibility, speeds up detection and coordinates response within the agreed scope. Protection also depends on implementation, staff behaviour, timely remediation and your organisation’s risk decisions.
Do you provide managed cyber security outside Melbourne?
Yes. Monitoring and investigation are delivered remotely, so we support businesses across Australia from our South Melbourne office.
